

Category Archives: CMMC
Why Waiting to Schedule Your Third-Party Assessment Will Create a Bigger Problem
When the Department of War (DoW) announced the pause on implementing CMMC Phase 2 (assessment)...
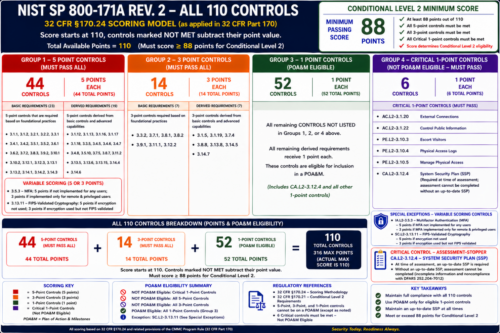
What Prime Contractors Needs to See from Your CMMC Self-Assessment
As CMMC continues through its phase 2 pause, one thing hasn’t changed: Organizations Seeking Certification...

CMMC’s RFI Opportunity and the Department of Defense
The Cybersecurity Maturity Model Certification (CMMC) journey has been years in the making. While many...
Think Your CMMC Self-Assessment Is Easy? Think Again.
The Department of War’s (DoWs) decision to remain in CMMC Phase 1 has changed the...

CMMC Phase 2 is Paused… Cybersecurity Isn’t
The Department of War’s (DoW) recent decision to suspend CMMC Phase 2 rollout (a move...
The Part of CMMC Nobody Talks About: Maintenance
Most conversations about CMMC Level 2 focus on one thing: Getting ready for the assessment....
CMMC at Scale: What Happens When Compliance Meets Reality?
The Cybersecurity Maturity Model Certification (CMMC) ecosystem is no longer theoretical. It is actively being...
Navigating The CCP/CCA/PI Certification Path
As the CMMC ecosystem expands, more professionals are asking the same certification questions: The challenge...
The 03.06 Incident Response Shift in Rev 3
We are going over the major changes in NIST 800-171 Rev 3 piece by piece...
There’s No Such Thing as Free Inheritance: The CMMC Estate Reality
When Organizations Seeking Certification (OSCs) begin preparing for CMMC, certain terms quickly become a part...