

Category Archives: Cybersecurity
Why Waiting to Schedule Your Third-Party Assessment Will Create a Bigger Problem
When the Department of War (DoW) announced the pause on implementing CMMC Phase 2 (assessment)...
What Prime Contractors Needs to See from Your CMMC Self-Assessment
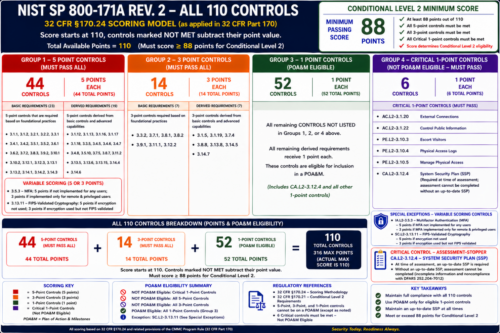
As CMMC continues through its phase 2 pause, one thing hasn’t changed: Organizations Seeking Certification...

CMMC Phase 2 is Paused… Cybersecurity Isn’t
The Department of War’s (DoW) recent decision to suspend CMMC Phase 2 rollout (a move...

CMMC at Scale: What Happens When Compliance Meets Reality?
The Cybersecurity Maturity Model Certification (CMMC) ecosystem is no longer theoretical. It is actively being...
The 03.06 Incident Response Shift in Rev 3
We are going over the major changes in NIST 800-171 Rev 3 piece by piece...
How to Prepare for the CMMC Rollout
The Reality of the CMMC Rollout As the CMMC rollout looms, many defense (war) contractors...
How Are CMMC and FedRAMP Related?
Are CMMC and FedRAMP the Same Thing? Short Answer: No. But they are closely related....
CMMC and The Creation of NIST 800-171
Dr. Ron Ross and The History of NIST 800-171 When it comes to federal cybersecurity...

The ‘Department of Defense’ Is No More
“We changed the name after World War II from the Department of War to the...
Can I Do CMMC Without Third-Party Assistance?
Internal CMMC Implementation as a Contractor Achieving internal CMMC (Cybersecurity Maturity Model Certification) Level 2...