

Receiving a CMMC certified status represents a significant milestone for organizations handling controlled unclassified information (CUI). Achieving this mandatory certification not only demonstrates compliance but also strengthens trust for government partnerships. However, many organizations are discovering that the CMMC assessment process is far more intricate than expected. Especially when faced with a dreaded “not met”…
Dr. Ron Ross and The History of NIST 800-171 When it comes to federal cybersecurity standards, few names carry as much weight as Dr. Ron Ross. Known as the “father” of NIST SP 800-171, Dr. Ross has been at the center of efforts to safeguard sensitive government data. Data that, while not entirely classified, could…

Why Contractors Should Reevaluate Their MSP’s CMMC Capabilities For contractors working with the Department of Defense (DoD), or more recently known as the Department of War (DoW), compliance is the gateway to future contract eligibility. One of the most critical partners in this journey is a vendor that is equipped to assist with your certification,…
An Introduction into the Complexities of Vulnerability Management For those interacting and living within CMMC compliant systems (MSPs and federal contractors alike), vulnerability management is one of the most complex, yet essential, components of achieving and maintaining Level 2 certification. It’s an ongoing process that demands the right tools, thoughtful planning, and a proactive approach…
The Complexities of the CMMC Assessment The Defense Industrial Base (DIB) is undergoing a critical transformation as cyber requirements tighten under current CMMC requirements. For organizations working within the DIB, preparing for CMMC assessments is a business necessity that directly impacts eligibility for government contracts. Yet, the path toward certification remains complex, with organizations often…

What Federal Contractors (And Their Subcontractors) Need to Know The recent release of 48 CFR has major implications for contractors and subcontractors working with the Department of Defense (DoD), or more recently known as the Department of War (DoW). These changes represent a turning point in federal cybersecurity/CMMC compliance, and the risks of overlooking them…
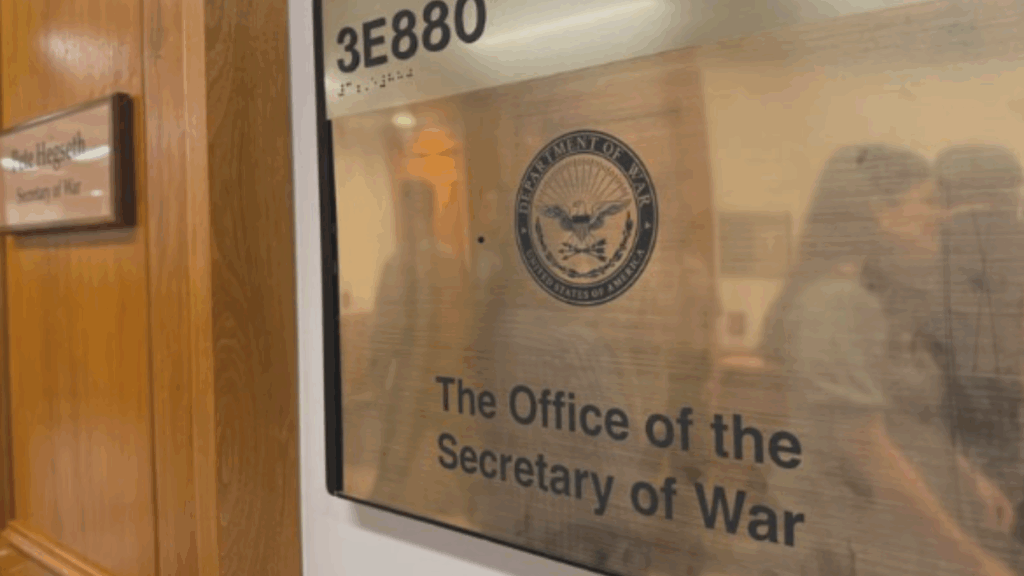
“We changed the name after World War II from the Department of War to the Department of Defense and … we haven’t won a major war since.” -Defense Secretary, Pete Hegseth Last week, President Donald Trump signed an executive order to officially change the name of the Department of Defense to ‘Department of War’ as…

Internal CMMC Implementation as a Contractor Achieving internal CMMC (Cybersecurity Maturity Model Certification) Level 2 status, as many know, is no small feat. It’s a comprehensive organizational journey that demands much more than just your basic IT upgrades. As organizations across the Defense Industrial Base (DIB) work towards their own CMMC compliance, key lessons are…
What Makes a Great System Security Plan? A system Security Plan is the backbone of organizational security. They are living documents that guide how an organization safeguards its information systems, especially when handling Controlled Unclassified Information (CUI). For businesses seeking to meet NIST 800-171 and CMMC requirements, understanding how to develop, maintain, and execute an…
A Quick Breakdown of the Critical Role of Data Flow Diagrams in CMMC Compliance When it comes to cybersecurity and compliance, few tools are as essential (and often underestimated) as data flow diagrams. For organizations working with Controlled Unclassified Information (CUI), the ability to visualize and manage how data moves through their systems is not…