

A lot of organizations start looking at NIST 800-171 Rev 3 and think to themselves:
“This isn’t required yet”
“We’re still being assessed for Rev 2”
“We’ve already built our SSP”
They think they have time, but they are sadly mistaken.
Rev 3 is coming in hot and when it hits, it will not be a light update… it will be a structural shift.
And the longer you wait to implement, the more difficult the transition will be.
“We will deal with it later”
It is tempting to treat NIST 800-171 Rev 3 like a future problem.
Understandably so. People are still being assessed for Rev 2.
However, the reality is that rev 3 is what CMMC has to look forward to.
Not preparing now= scrambling later
And scrambling in CMMC never ends well.
This isn’t just your run-of-the-mill update.
This is changing how controls are structured, assessed, and documented.
Fewer controls but… double the work?
At first glance, NIST 800-171 Rev 3 can look easier.
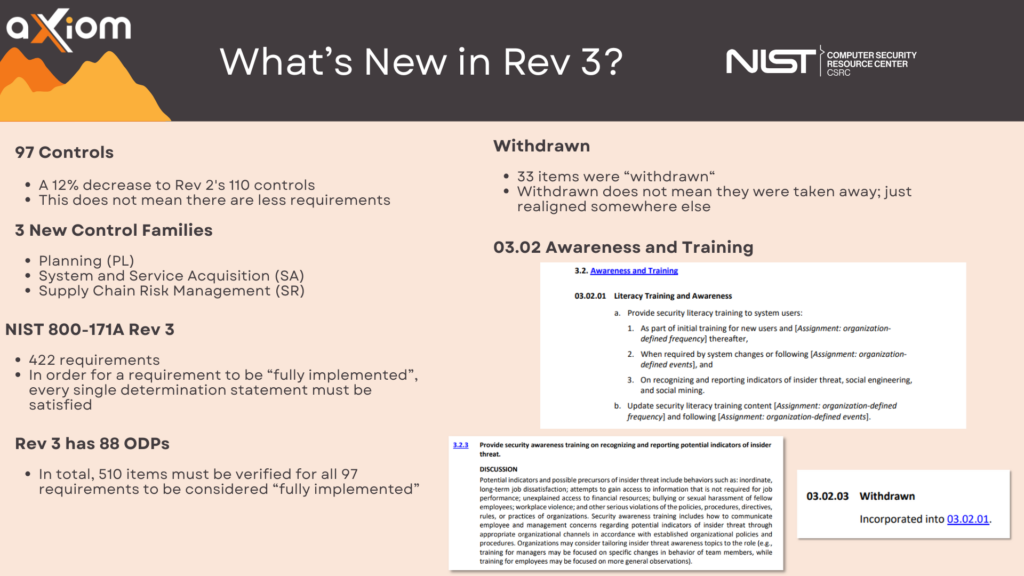
Only 97 controls instead of 110: sounds like a win.
Until you dig a little deeper… Rev 3 has expanded to:
- 510 assessment objectives rather than 320
- More details
- More specifics
- More expectations
So, while controls did go down, the actual work went way up.
“Just Convert Your SSP”… It’s a Trap!
A lot of teams ask: “Why can’t we just convert our Rev 2 SSP to Rev 3?”
Because controls have been consolidated.
Content has moved and new expectations were added.
Entire sections don’t map properly.
And simple copying and pasting your Rev 2 SSP into Rev 3 will turn into gaps, confusion, and frustration.
Controls are Bigger, Not Simpler
Rev 3 didn’t remove complexity, it compressed it.
Multiple controls from Rev 2 are now:
- Merged into single controls
- Expanded with more detailed expectations
- Backed by significantly more assessment objectives and ODPs
This means you can’t skim on controls, and you have to track every objective inside them.
Miss one and you miss compliance.
ODPs are the Decider… Not You
Rev 2 gave organizations very loose flexibility.
Rev 3 has taken a lot of that away.
Enter: Organizational Defined Parameters (ODPs)
These define things like:
- Training frequency
- Timeframes
- Specific conditions
And here’s the kicker… You don’t fully control those definitions anymore.
The Department of War sets them.
And you are required to align to what they say.
So now it’s not just: “Define your process”.
It’s: “Implement their definition into your process”.
“We Already Do This” Isn’t Enough
Organizations think that “We already train users” and “We already have policies” is enough…
It’s not.
Now you have to:
- Prove each objective is covered
- Show how it’s covered
- Map it clearly in your SSP
- Demonstrate it to an assessor
Only doing the work ≠ documenting it correctly.
A Greater Impact Than Just Your SSP
If you’re an MSP, this isn’t just your client’s problem.
Rev 3 affects:
- Your System Security Plan (SSP)
- Your Customer Responsibility Matrix (CRM)
- Your service boundaries
- Your documentation expectations
If your CRM isn’t mapped to assessment objectives… it will not hold up.
Start Now or Catch Up Later
You don’t need to finish everything tomorrow.
But you do need to start.
Because when Rev 3 becomes the standard, the organizations that already understand it will be moving forward.
And everyone else will be trying to catch up.
The Real Takeaway
Rev 3 isn’t harder because it’s bigger.
It’s harder because it’s clearer.
It removes some ambiguity and increases accountability.
And that is what CMMC has been moving toward since the beginning.
If you’re navigating the shift from Rev 2 to Rev 3 and want help breaking it down in real terms, check out our podcast, Climbing Mount CMMC. Or reach out on our website. We would love to talk.